Peoplesoft Hhc helps organizations manage health-related workflows with stronger controls, auditability, and operational consistency. This objective guide explains what the keyword typically refers to in enterprise systems, how implementation choices affect data quality and compliance outcomes, and what teams should prepare before rollout. The article also covers supplier-side considerations, conditions, and common questions from system owners.
When organizations talk about Peoplesoft Hhc, they usually refer to a PeopleSoft-driven approach used to support health-related administrative processes—such as claims-adjacent workflow handling, eligibility-style logic, reporting structures, and controlled access to sensitive data. From an industry-expert perspective, the practical value of PeopleSoft in an HHC (health-focused) context comes from configuration discipline, data governance, and repeatable operations. The very important implementation takeaway is simple: the system’s effectiveness is determined less by the interface and more by how master data, security roles, and workflow rules are defined and sustained over time.
In many enterprises, this shorthand becomes a way to describe a whole operational philosophy: treat PeopleSoft not merely as a software product, but as the system that standardizes how decisions are executed and recorded across teams. That philosophy can become the difference between a workflow system that is consistently reliable and one that devolves into tribal knowledge, spreadsheets, and manual exceptions that never fully reconcile with “system truth.” In health-adjacent administrative environments—where accuracy, auditability, timeliness, and traceability are not optional—those differences matter.
In many enterprises, PeopleSoft modules (or PeopleSoft-integrated components) are used to standardize processes that involve protected health information, time-bound transactions, and multi-step approvals. In that setting, “Peoplesoft Hhc” is commonly used as shorthand for an operational pattern: PeopleSoft as the workflow backbone, with structured data models and reporting layers aligned to health-administration needs.
Because terminology varies across industries and vendors, you should treat “Peoplesoft Hhc” as a context label rather than a single universally defined product. The meaning becomes clear only after you map the organization’s actual scope: which transactions are processed, which reports are required, which integrations feed the system, and what audit trail expectations exist for your environment.
To make that mapping concrete, teams often break “HHC” work into categories that PeopleSoft can support. For example:
When PeopleSoft is used to unify these categories, “Peoplesoft Hhc” becomes shorthand for a controlled enterprise workflow environment, where each step is logged, permissions are enforced by role, and changes to critical data follow governance processes rather than ad-hoc edits.
Organizations often ask about “price information” when evaluating PeopleSoft-related initiatives. In practice, the true cost profile is determined by implementation complexity: integrations, data cleansing, security design, workflow tuning, and ongoing support. Even when pricing is quoted by a supplier, the operational impact typically hinges on requirements clarity and change management readiness.
As an expert, I recommend treating price information as one input, not the decision driver. A well-scoped PeopleSoft HHC rollout with strong governance tends to reduce rework, shorten the time to stable operations, and lower the cost of future changes.
It’s also important to separate the cost of the initial delivery from the cost of long-term ownership. In health-adjacent workflows, ownership cost frequently grows in predictable areas:
Therefore, the most cost-effective approach is frequently the one that reduces uncertainty and ensures that each component of the system (data, roles, workflows, reporting, integrations) can be maintained without rewriting the entire system every time requirements evolve.
Supplier-side capabilities frequently determine whether the Peoplesoft Hhc program remains maintainable. When evaluating suppliers, look beyond marketing and confirm the presence of practical competencies such as:
These factors directly affect whether PeopleSoft HHC operations remain stable once the project transitions from implementation to everyday execution.
In practice, suppliers often distinguish between “build” work and “stabilize” work. For PeopleSoft HHC, stabilization is not a side phase; it is a major portion of what determines success. Stabilization includes:
When suppliers can demonstrate experience in these areas (ideally via case studies and deliverable samples), you reduce your risk of inheriting a system that behaves unpredictably after go-live.
Across very PeopleSoft HHC programs, the following building blocks tend to determine success:
Health-related workflows are highly sensitive to data quality. Master data—such as organizational hierarchies, personnel identifiers, plan or policy-like reference tables, eligibility-style rules, and code sets—must be maintained with controlled change procedures.
In many organizations, the hardest part is not building PeopleSoft configuration—it’s agreeing on who owns data. For example, one department may believe that eligibility reference tables are “static,” while another department treats them as frequently changing. Without clarity, you end up with ambiguous ownership where changes occur through informal channels or delayed approvals.
To strengthen governance, teams commonly implement these practices:
In a PeopleSoft HHC environment, governance also extends to “non-master” data that becomes operationally critical—such as workflow statuses, audit reasons, decision codes, and documentation attachments. If those fields aren’t governed with the same rigor as master data, auditability becomes fragile and reporting may diverge from operational reality.
PeopleSoft can support granular access, but the organization must define roles that match operational reality. For HHC-adjacent workflows, segregation of duties is typically crucial: the user who initiates actions should not be the same user who approves sensitive outcomes, unless your internal controls explicitly justify and document exceptions.
When role definitions are vague, security becomes a source of operational friction. Users may request broader permissions “to avoid getting blocked,” and over time roles can inflate. Alternatively, roles may become too restrictive, causing excessive manual workarounds.
Strong security design in PeopleSoft HHC usually includes:
In addition, teams often need to consider “break-glass” access for emergencies. While sensitive health-adjacent systems should not allow casual emergency access, organizations still require a documented and monitored process for incidents where the normal workflow cannot proceed.
Real operations involve edge cases. The system should be configured to handle exceptions predictably—through status management, logged actions, and clear escalation routes.
If workflow rules only handle the “happy path,” organizations typically experience operational overload after go-live. Staff eventually encounter situations such as missing data, conflicting eligibility indicators, conflicting effective dates, documentation that arrives late, or cases that must be corrected due to upstream system errors.
Therefore, exception handling should be treated as a first-class design requirement. A robust PeopleSoft HHC workflow typically defines:
In practice, well-designed exception handling reduces the need for manual spreadsheets and enables faster investigations when audits or internal reviews occur. Instead of trying to reconstruct decisions from memory, teams can reference system evidence and status history.
Even when the system functions perfectly, organizations can struggle if reporting is not aligned to how audit and operational teams actually review transactions. Traceability should be built into the process rather than added afterward.
Reporting in PeopleSoft HHC environments commonly includes both operational monitoring and compliance evidence. Operational teams often need:
Compliance and audit teams often require:
To avoid reporting rework, many organizations implement report acceptance criteria early. That means defining sample cases and verifying that report outputs match what operational teams expect to see during reviews. In other words, “report correctness” is not just technical query validity; it’s operational meaning.
Below is a practical, step-by-step path you can adapt. While vendors and organizations may use different terminology, the sequence generally reflects industry top practice for PeopleSoft-based enterprise deployments.
To make this generic guide more actionable, it’s helpful to treat each step as a “deliverable + evidence” checkpoint rather than a purely procedural milestone. For instance:
That evidence-driven approach often prevents late-stage surprises and allows procurement stakeholders to evaluate readiness in a transparent way.
Because “Peoplesoft Hhc” programs can vary widely, the table below summarizes typical conditions you should confirm with stakeholders and suppliers. It is deliberately phrased as a comparison to help you negotiate clarity during procurement and rollout planning.
| Area | What to confirm (typical requirement) | Why it matters for PeopleSoft HHC | How to verify |
|---|---|---|---|
| Scope definition | Which workflows and data objects are included, and what systems remain external | Prevents rework and reduces integration ambiguity | Signed-off scope document and interface inventory |
| Security model | Role matrix, segregation of duties, and audit trail expectations | Protects sensitive health-related records and decision logging | Role testing and sample audit report review |
| Data governance | Master data ownership, change controls, and validation rules | Improves accuracy of operational decisions | Data stewardship workflow and test data validation results |
| Integration approach | Mapping rules, error handling, reconciliation, and monitoring | Reduces silent failures and data drift | Interface tests, reconciliation scripts, and monitoring runbooks |
| Reporting needs | Operational and audit reporting list, refresh schedules, and permissions | Ensures traceability and day-to-day usability | Report acceptance criteria and sample report walkthroughs |
| Operational readiness | Support model, escalation paths, incident and change procedures | Stabilizes operations after go-live | Readiness checklist and dry-run rehearsals |
| Supplier responsibility | Deliverables, handover artifacts, warranty/support terms | Clarifies accountability for defects and improvements | Statement of work review and acceptance criteria mapping |
To strengthen procurement alignment, consider adding two “missing” requirement areas that are often overlooked in earlier drafts: data retention and historical reconstruction, and testing strategy depth (not just unit tests, but scenario tests and negative tests). Both directly influence audit outcomes and operational confidence.
For example, if your workflow decisions need to be reproducible for regulatory inquiries, then your design must specify how long key records and evidence remain accessible, what historical states remain viewable, and how corrections are documented without overwriting prior evidence.
Enterprise software used in health-focused operations typically must support controlled access, auditability, and repeatable processes. PeopleSoft environments are often selected for their enterprise capabilities and structured data handling. However, software capability does not automatically produce compliance outcomes; rather, compliance depends on configuration, process design, and ongoing operational controls.
For objective grounding, you can review general guidance on auditability, information security, and identity controls from recognized frameworks. For example, the National Institute of Standards and Technology (NIST) provides widely referenced guidance on security and risk management practices for organizations, which can inform security design and monitoring decisions. (See: NIST publications such as the NIST Cybersecurity Framework and related NIST security guidance.)
In regulated or health-adjacent environments, the operational reality often includes multiple stakeholders: operations teams that process transactions, compliance teams that validate controls, internal audit teams that inspect evidence, and sometimes external partners that send or receive data. “Peoplesoft Hhc” should be evaluated in that multi-stakeholder context—meaning you should validate that each stakeholder can accomplish their responsibilities using system evidence.
There is also a common misassumption: that achieving compliance requires only “security and audit logs.” In practice, audit readiness also depends on:
PeopleSoft can support these needs, but the organization’s operational design—how you define controls, measure performance, and manage changes—determines the outcome.
Even with a capable supplier, the risks tend to cluster around a few recurring themes:
The top mitigation strategy is not a single tool; it is governance plus disciplined change control.
To expand on these risks and mitigation patterns in a PeopleSoft HHC context:
In a PeopleSoft HHC program, risk management is therefore inseparable from operational discipline. If you treat risk as an afterthought, you may create a system that is functional but fragile. If you treat it as a design input, you build a platform that stays reliable as business processes evolve.
You requested localization behavior when a city or country appears in keywords; however, no specific city/country text was provided to convert. Still, localization matters in practice. In health-focused enterprises, teams often rely on local operating rhythms—such as internal scheduling norms, regional compliance practices, and communication styles between operations and compliance units. If your rollout is “nearby” to a regional operating center, incorporate that center’s actual review cycles into reporting refresh schedules and training timelines. That is often more influential than language-only localisation.
Localization in enterprise workflows can include factors beyond language—such as:
When PeopleSoft HHC is deployed across multiple regions, you often want to avoid building region-specific custom workflows unless absolutely necessary. Instead, consider using configuration parameters, reference data sets, and environment-specific settings where appropriate. That reduces the operational complexity of maintaining multiple variations of the same workflow.
Also consider cultural localization in training: even when system behavior is identical, the way users are trained to handle exceptions may differ. The training should mirror local operational practice while still enforcing the centralized governance requirements that protect audit integrity.
To make your evaluation objective, ask suppliers for evidence tied to outcomes rather than promises. Consider requesting:
This turns the supplier discussion into a demonstrable technical plan that aligns with operational reality.
To deepen that procurement approach, you can expand the checklist into “proof of capability” prompts. Instead of asking “Can you do integration monitoring?”, ask:
Similarly, for security, ask suppliers to demonstrate how roles are validated. For example:
For workflow, you can ask for evidence of exception handling maturity:
Finally, procurement should include operational readiness commitments:
By structuring supplier questions around evidence, you reduce the risk that you approve a plan based on vague statements rather than demonstrated capability.
“Peoplesoft Hhc” is commonly used as shorthand for a PeopleSoft-enabled approach to health-related administrative workflows. The precise meaning depends on your organization’s scope, including which transactions are processed, what data objects are governed, and which integrations are included.
Not necessarily. Many programs aim to minimize custom code by using structured configuration, well-defined workflows, and disciplined master data governance. Heavy customization is sometimes unavoidable, but it should be justified by clear requirements and evaluated for good maintainability.
When you do need customization, a good practice is to constrain it. Constrain means: keep custom logic limited in scope, document it thoroughly, and ensure it is wrapped in configuration or patterns that remain easy to update. Also insist on regression test coverage that proves custom logic doesn’t break after PeopleSoft updates.
Price should be evaluated alongside scope clarity, integration complexity, security design depth, reporting acceptance criteria, and the supplier’s operational readiness deliverables. Lower initial cost can become expensive if it leads to rework, incomplete data governance, or fragile integrations.
To improve pricing evaluation, ask for pricing by work package and clarify what is included in each package. For example, differentiate between:
This approach makes cost comparisons fairer and reduces the risk of surprise costs late in the project.
Typical causes include incomplete scope definition, delays in data cleansing and master data approvals, underestimated integration testing effort, and late security role validation. Strong governance and early test planning reduce these delays.
To preempt delays, many teams set up early “dependency lanes” for the most common blockers:
Traceability typically depends on workflow logging, controlled status transitions, and secure role permissions. To ensure audit readiness, teams should validate that key transactions and approvals can be reconstructed through system records and reporting outputs.
Auditability is strongest when the workflow design enforces that audit-relevant decisions always pass through controlled approval states. If decisions can be made through loosely controlled paths—such as manual updates that bypass workflow—then audit reconstruction becomes harder and evidence becomes inconsistent.
When validating audit readiness, ask reviewers to attempt “reconstruction exercises” on sample cases. Give them a case identifier (or a set of sample criteria) and require them to reconstruct what happened, who approved it, why, and when. If they cannot do it easily using system outputs, that’s a design gap rather than a documentation gap.
Organizations usually need a production support model that includes monitoring procedures, incident escalation, change management workflows, and regular review of workflow exceptions. A supplier should provide handover artifacts such as runbooks and knowledge transfer materials.
Operational support should also include a stabilization period with clear acceptance thresholds. For example, define what constitutes a stable workflow performance baseline, how often reconciliation checks are run, and what severity levels trigger supplier involvement vs. internal handling.
Yes. Many organizations use established guidance such as NIST security and risk management frameworks to structure identity, access, monitoring, and risk controls. You should align your design to your organization’s regulatory and internal requirements.
Beyond NIST, organizations may map controls to internal policies or other governance frameworks. The key is not the framework name, but the ability to show that your PeopleSoft HHC design supports those control objectives—especially around identity, authorization, logging, monitoring, and risk management.
In many cases, yes. However, successful integration depends on careful data mapping, reconciliation logic, robust error handling, and monitoring. Integration should be treated as an operational capability, not just an interface build.
It’s common for integration failures to be discovered only when reporting outputs look wrong. To avoid that, integrate monitoring and reconciliation early, and create operational dashboards that show both message processing health and data correctness indicators. In a health-adjacent environment, the cost of silent failure is high because downstream decisions may depend on incomplete or incorrect upstream updates.
For organizations evaluating Peoplesoft Hhc, the core message is that success comes from rigorous requirements definition, disciplined configuration, and good governance—not from interface polish alone. When supplier engagement focuses on security design, data governance, integration monitoring, and operational readiness, PeopleSoft becomes a stable platform for health-related administrative workflows. If you approach implementation with structured planning and measurable acceptance criteria, you can reduce operational friction and build a system that supports day-to-day decision-making with confidence.
In other words, treat “Peoplesoft Hhc” as an enterprise operating model: a set of practices that turn complex, sensitive workflow needs into repeatable actions with strong audit traceability. When your organization invests early in master data ownership, segregation of duties, exception handling, and evidence-oriented reporting, the PeopleSoft environment becomes resilient under real operational pressure—where edge cases appear, systems evolve, and audits happen whether you are ready for them or not.
Organizations that succeed tend to ask one consistent question throughout delivery: “Can we prove system truth?” If you can reconstruct decisions, approvals, and data lineage using system records and reporting outputs—and if you can do so quickly for both operational reviews and audits—then you’re not just implementing software. You’re implementing reliable enterprise health workflow operations.
For general security and risk management context, see the National Institute of Standards and Technology (NIST) publications, including the NIST Cybersecurity Framework and related NIST guidance on security controls and risk management practices. These resources support objective alignment of identity, access control, monitoring, and governance requirements, which are relevant to secure enterprise deployments.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Explore the Tranquil Bliss of Idyllic Rural Retreats
How to Make Lasting Memories at Disneyland Attractions
4rkojvsx Technology: Industry Insights and Buying Guide
Affordable Phones and Plans for Seniors
Affordable Full Mouth Dental Implants Near You
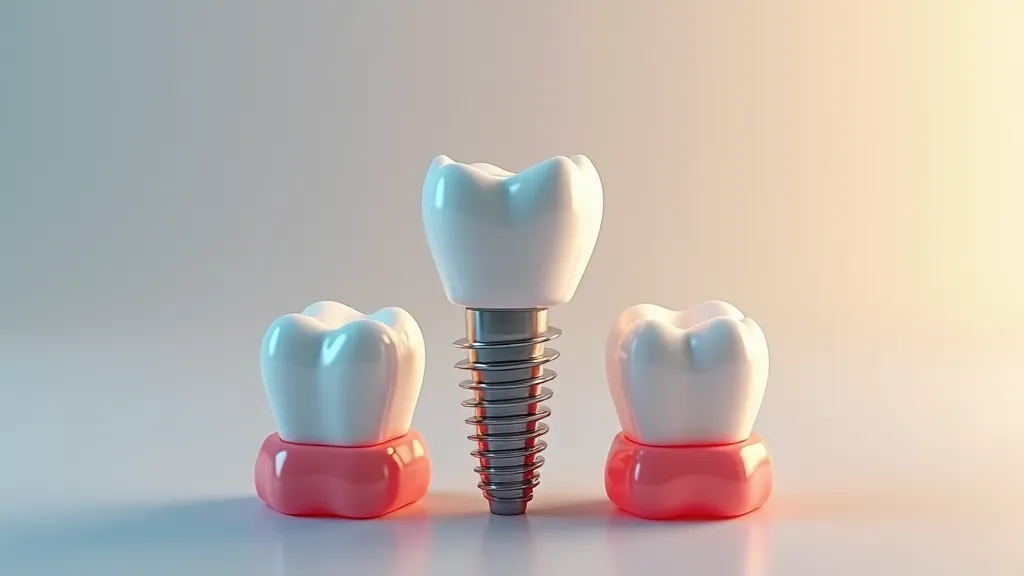
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Discovering Springdale Estates
Unveiling RS Sul Telecom Services
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Finding an optimal mix of insurance premiums and direct medical costs is crucial for effective healthcare budgeting. This discussion will delve into tactics to achieve a balance that aligns with your finances.
4rkojvsx Technology: Industry Insights and Buying Guide
This guide explains 4rkojvsx with an evidence-based, step-by-step approach to evaluating suppliers, pricing, and requirements before purchasing. Objectively, the term points to a technical category where compatibility, quality controls, and documentation matter as much as the nominal price. Readers will also find a practical comparison table, conditions, and targeted FAQs.
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Selecting an adept dentist is critical for ensuring the efficacy and your satisfaction during a dental implant procedure. This in-depth guide is designed to assist you in finding a dental expert who meets your personal requirements, guaranteeing that your path to dental implant success is seamless and fruitful.

Protect Your Perfect Smile: Master the Art of Defending Your Teeth Against Acid Attacks
Though they may tantalize the palate and invigorate the senses, foods and drinks with high acid content are a double-edged sword with regard to oral wellness. Continual exposure to these substances progressively strips away the protective enamel from our teeth, which can lead to increased sensitivity, changes in coloration, and a variety of other dental complications. This composition offers insight into relishing these zesty favorites while safeguarding your teeth from damage.
Comprehensive Insight into Boob Enhancement
Boob enhancement is a cosmetic procedure aimed at augmenting the size and improving the shape of breasts for aesthetic purposes. With the evolution of medical procedures, this enhancement has become more sophisticated, offering various options to cater to individual preferences and needs. This detailed guide explores the intricacies of boob enhancement, tackling myths, benefits, and expert advice to help potential candidates make informed decisions.
Pmoc Abrava: Supply, Pricing, and Quality Guide
This guide explains what “Pmoc Abrava” is used for in professional settings and how suppliers evaluate quality and consistency. It offers an objective overview of common procurement considerations, documentation, and verification practices. Readers will also find a comparison-style supplement section and practical requirements before choosing a source.