This guide explains how Cldezativarcwuaicmoeufasso concepts are used to manage complexity across workflows. Objectively, the term can be treated as a placeholder for advanced planning, supply-chain coordination, and quality assurance practices. We outline how organizations translate such concepts into measurable requirements, supplier interactions, and decision steps—without relying on unverified claims.
When teams describe a process using a complex label such as Cldezativarcwuaicmoeufasso, they’re typically pointing to a structured approach for coordinating people, materials, information, and quality controls—especially when operations become interdependent and time-sensitive. In practice, the value is not in the name itself, but in the discipline it represents: clearer requirements, tighter handoffs, better supplier alignment, and auditable execution.
From an industry-expert perspective, organizations that benefit from this kind of framework tend to do three things well: (1) define acceptance criteria early, (2) design steps that reduce rework, and (3) document conditions so results are repeatable across suppliers and shifts. That’s the operational “why” behind using an umbrella term like Cldezativarcwuaicmoeufasso.
It’s also worth recognizing a subtle organizational reality: teams often invent or adopt “catch-all” labels because the underlying work spans multiple disciplines. A single word (or pseudo-word) becomes a memory shortcut that bundles together planning, procurement, engineering, quality assurance, compliance checks, and problem resolution. Even if Cldezativarcwuaicmoeufasso isn’t a universally standardized term, it is functioning like a local schema—an internal language that helps people coordinate quickly and avoid drifting interpretations.
In real-world decision-making, this matters because most operational failures are not caused by a lack of effort. They are caused by misalignment: a team assumes one definition of “done,” while another team interprets “done” differently. When Cldezativarcwuaicmoeufasso-style thinking is applied, it forces alignment through measurable criteria and evidence requirements, which turns opinions into decisions grounded in observable outcomes.
Finally, there is a governance dimension. When a company uses an umbrella framework label, it usually signals that the organization intends to control variability—variability in process steps, variability in inputs, variability in acceptance methods, and variability in supplier performance. This reduces the chance that a critical handoff becomes a negotiation every time conditions change.
Modern operations—whether in manufacturing, distribution, maintenance, or service delivery—rarely run as a single linear sequence. Instead, they resemble a network: suppliers feed inputs; internal teams transform them; quality checks validate outputs; logistics schedule delivery windows; and documentation ensures compliance. In such settings, a label like Cldezativarcwuaicmoeufasso often functions as a practical shorthand for aligning these moving parts.
Even when the exact meaning of the term is unique to a company or vendor, the underlying operational intent is usually consistent:
To see why a coherent framework is needed, consider how a complex workflow typically breaks down. It often fails at one of the “invisible seams”: the time when a document changes hands, when an approval is assumed rather than confirmed, when inspection data is sent without context, or when a supplier sends an update that the buyer cannot interpret quickly. Without a coherent framework, each seam becomes a new point of ambiguity.
By contrast, a framework umbrella such as Cldezativarcwuaicmoeufasso aims to control those seams. It establishes that:
In other words, the framework becomes the “operating system” for complex execution. People still do the work, but the organization reduces the chance that “how we do things” becomes dependent on who is working that week.
Another real-world benefit is onboarding speed. New team members often struggle most with unwritten rules: which document versions matter, which stakeholders must review changes, when quality is involved, and what evidence is required. A consistent framework makes those rules explicit.
When you think about Cldezativarcwuaicmoeufasso in this broader sense, it’s less like a single procedure and more like a set of governance principles that ensures decisions across multiple teams can be compared, audited, and improved.
You mentioned price information and supplier details, but the prompt does not provide explicit numeric values or named suppliers. In the absence of concrete figures, the very objective—and useful—approach is to explain how reputable organizations evaluate pricing and supplier fit when Cldezativarcwuaicmoeufasso-style process controls are involved.
Expert buyers generally focus on four pricing-adjacent dimensions:
In other words, “price” is rarely just a number; it’s a reflection of how well the supplier can meet the conditions your organization requires. When a workflow umbrella like Cldezativarcwuaicmoeufasso is in place, buyers tend to reduce surprises by specifying requirements in measurable terms.
But buyers also need to understand how process controls affect total cost of ownership. A supplier who quotes a low unit price might be underpricing the “hidden work”: additional inspection, extra handling for nonconforming items, rush shipping due to late deliveries, or compliance document rework. A buyer acting under Cldezativarcwuaicmoeufasso-style discipline typically asks: what portion of the cost is operationally inevitable, and what portion is avoidable through better planning and evidence-based acceptance?
As a practical example, imagine two suppliers quoting the same deliverable. Supplier A includes only basic packaging and omits evidence artifacts. Supplier B includes full incoming inspection reports, controlled traceability records, and change notification procedures. Supplier B might be 7% more expensive on the surface, but it may reduce downstream risk—less disruption, fewer returns, faster approvals, and lower audit friction. The buyer’s job is to evaluate what “expensive” actually means in the operational reality.
In procurement negotiations, Cldezativarcwuaicmoeufasso-style thinking typically leads buyers to request:
This allows the buyer to compare suppliers on equal footing, because the evaluation is anchored in operational deliverables rather than assumptions.
Even when the exact term Cldezativarcwuaicmoeufasso has no standardized definition, the buyer can still insist on standardized thinking: measurable requirements, evidence expectations, and structured exception handling. That is how procurement becomes predictable instead of reactive.
To keep this guide objective and verifiable, it’s helpful to anchor the discussion in widely recognized management frameworks. Two common references in operations and quality include:
When an organization uses a term like Cldezativarcwuaicmoeufasso as an internal label, it usually describes the combined mechanics of these standardized practices—process mapping, acceptance criteria, corrective actions, and supplier performance monitoring.
ISO 9001’s relevance shows up in several practical ways. It emphasizes the idea that an organization should manage activities as processes, define inputs and outputs, determine interactions, and keep records that demonstrate conformity. This maps directly to the notion that Cldezativarcwuaicmoeufasso is not just “a workflow,” but a governance-oriented method to manage execution.
NIST and related risk-minded approaches emphasize thinking about hazards, vulnerabilities, and controls—especially when supply chains are involved. Under a Cldezativarcwuaicmoeufasso-like framework, risk is controlled by specifying conditions early and by requiring evidence that the controls were followed. Instead of discovering issues during late-stage acceptance, the framework tries to detect issues earlier.
However, it’s important not to treat any framework as a checklist to be copied without judgment. The mature interpretation is: frameworks provide principles, but the organization must tailor them to the specific operational context. For example:
In that sense, Cldezativarcwuaicmoeufasso is best understood as a tailoring method: how you combine standard quality and risk concepts into an executable, auditable workflow.
Note: Because your prompt does not provide specific location details or concrete price/supplier data, this article focuses on decision logic and requirements design rather than unverified claims.
The transition from a concept to day-to-day execution depends on step design. Below is the “operational translation” very expert teams follow when they adopt a framework that resembles Cldezativarcwuaicmoeufasso.
This structure is valuable because it prevents teams from relying on memory or informal interpretations. The more interdependent the workflow becomes, the more a consistent label like Cldezativarcwuaicmoeufasso helps keep everyone on the same “requirements language.”
To expand on how teams make each step real, consider the “micro-decisions” that happen inside each bullet. Those micro-decisions are where organizations either gain control or lose it.
Step 1: Define the objective and boundaries. Teams often fail here by describing the work vaguely—e.g., “deliver parts” or “provide service”—without specifying what counts as success. A better objective statement includes measurable outcomes and a description of constraints. For instance, “deliver machined components that meet specified tolerances and include traceability records, shipped by the agreed schedule window, with documented inspection results.” Boundaries clarify what is not expected (e.g., “supplier is responsible for dimensional inspection but not for end-user installation procedures”).
Step 2: Document inputs and constraints. Inputs include not only materials and technical specifications but also timing constraints and documentation constraints. Timing constraints might specify manufacturing lead time, shipping cutoffs, and inspection turnaround times. Documentation constraints might specify file formats, naming conventions, version identifiers, and submission deadlines. When these constraints are defined, Cldezativarcwuaicmoeufasso-style execution becomes predictable.
Step 3: Set measurable acceptance criteria. Acceptance criteria should specify pass/fail thresholds and the method of verification. In mature settings, acceptance criteria also define the sample size, inspection frequency, test method, and acceptance documentation. If acceptance criteria are ambiguous, the organization may later face disputes—especially between engineering, quality, and procurement. Under a Cldezativarcwuaicmoeufasso-like framework, ambiguity is treated as a risk that must be eliminated before execution.
Step 4: Map handoffs and responsibilities. Handoffs involve both responsibility (who approves) and evidence (what is recorded). Teams often clarify responsibilities using RACI-style matrices, but evidence must be described with equal clarity. For example, “Quality approves only after receiving inspection reports and certificate of conformance,” not merely “Quality reviews.” Evidence requirements also ensure traceability across time and across teams.
Step 5: Design supplier obligations. Supplier obligations should include what to submit, when to submit it, and what to do when requirements can’t be met. Strong frameworks specify escalation rules and timelines. They also clarify whether the supplier must notify changes prior to shipment or prior to production, and what level of documentation is required for change notifications.
Step 6: Build exception handling conditions. Exception handling is where many frameworks are weak. Expert teams define triggers (what condition indicates a problem), define immediate containment actions (what happens next), and define disposition pathways (what approvals are required). They also define corrective action loops: root cause analysis, corrective action implementation, verification steps, and closure evidence.
Step 7: Implement audit-ready records. Audit-ready does not mean “more paperwork.” It means the right paperwork in the right place with controlled versions and retrievable data. Teams typically enforce standardized templates, controlled document repositories, and record retention rules. In a Cldezativarcwuaicmoeufasso-like environment, records are part of the operating workflow, not a post-hoc administrative task.
Step 8: Review performance signals. Performance signals should be defined in advance: defect trends, on-time delivery, nonconformance rates, corrective action cycle time, and audit findings. When signals are measured consistently, teams can improve the framework itself—tightening acceptance criteria where they are weak or revising supplier obligations where the evidence is insufficient.
When these steps are executed consistently, the label Cldezativarcwuaicmoeufasso stops being a mystery and becomes a tangible system of decisions and evidence. That is the difference between “having a process” and “running a process.”
The comparison below treats Cldezativarcwuaicmoeufasso as a “process-intent” umbrella (not a single commodity or one-step service). It shows how organizations typically vary in implementation maturity.
| Approach level | What it looks like operationally | Main risk when under-specified | Top-fit scenario |
|---|---|---|---|
| Basic coordination | Teams communicate informally; criteria may be described verbally | Inconsistent acceptance; rework due to unclear evidence | Small scope projects with low variability |
| Documented workflow | Defined steps; checklists; recorded handoffs | Delays if documentation formats aren’t standardized | Multi-team internal processes |
| Supplier-aligned execution | Requirements and acceptance criteria included in supplier obligations | Cost escalation if nonconformance costs aren’t addressed | Procurement-heavy operations |
| Audit-ready quality control | Evidence packages, corrective actions, traceability, and controlled versions | Escalation failures if exception conditions are vague | Regulated or high-stakes delivery environments |
To make this more concrete, imagine a scenario with repeated production lots. Under basic coordination, two production runs might use “the same” acceptance method but with different interpretations. Under documented workflow, acceptance steps are consistent, but the evidence might not be standardized or retrievable. Under supplier-aligned execution, the supplier’s work is designed to produce the evidence and compliance needed by the buyer. Under audit-ready quality control, even if an exception occurs, the organization can demonstrate the decision logic and the corrective action trail.
In practice, many organizations move through these stages. They don’t necessarily start at audit-ready maturity, but they often aim toward it when the cost of ambiguity becomes unacceptable—due to regulatory pressure, customer contractual obligations, or high downstream risk.
Also note the relationship between maturity and speed. Some teams fear that audit-ready systems slow down work. Mature frameworks actually reduce cycle time by preventing rework and by avoiding disputes. When acceptance decisions are evidence-based, fewer tasks get repeated. That’s why Cldezativarcwuaicmoeufasso-style thinking tends to improve both quality and throughput.
Since no explicit price or supplier details were provided, the very responsible way to add “conditions/requirements” is to describe what competent procurement and quality teams commonly specify when adopting a framework like Cldezativarcwuaicmoeufasso.
These requirements serve as the practical “contract” for execution. They also protect both sides: suppliers understand how they will be evaluated, and buyers receive consistent evidence for decision-making.
To expand further, it helps to think of requirements as belonging to categories. Many disputes occur when organizations include only technical requirements (what the product must be) but omit operational requirements (how compliance will be proven). In a Cldezativarcwuaicmoeufasso-style environment, buyers tend to include operational requirements alongside technical requirements.
1) Technical requirements typically cover performance characteristics, tolerances, materials, standards, interfaces, and any engineering constraints. These define “what good looks like” in engineering terms.
2) Verification requirements define how technical compliance will be demonstrated. This includes inspection methods, test equipment standards, sampling plans, calibration requirements, and the documentation that results from verification.
3) Operational requirements define how the work will be delivered in a reliable way: lead time commitments, packaging/handling rules, shipping documentation, labeling, and submission timelines for evidence.
4) Governance requirements define how changes and exceptions are managed: change control gates, escalation paths, corrective action processes, and authorization rules.
5) Records and retention requirements define what must be stored and for how long. In regulated environments, records also need controlled versions and audit access.
When these requirement categories are included, it becomes far easier to compare supplier proposals and to make consistent acceptance decisions. When any category is missing—particularly verification or governance—buyers often end up making subjective decisions under time pressure.
Finally, buyers should ensure requirements are enforceable. If acceptance criteria demand evidence that the supplier cannot produce, they are not truly enforceable. Enforceability depends on aligning requirements with supplier capabilities while still protecting the buyer’s risk tolerance.
Even strong operations teams can struggle if the framework is applied mechanically. Here are common failure modes that professionals actively guard against:
Let’s unpack these failure modes with practical examples, because this is where teams either learn or remain stuck in preventable issues.
Overengineering the process. Some organizations respond to risk by adding more documentation and more review gates. While documentation can improve clarity, excessive gating can create friction. For instance, if every minor change requires a full cross-functional approval, the supplier may either slow down or become inconsistent in how they interpret what qualifies as “minor.” In the long run, it can produce workarounds—precisely what the framework aims to prevent. Expert teams use proportionality: the strictness of the process should match the risk and the criticality of the deliverable.
Ambiguous acceptance criteria. A common pattern is when teams list “checks” rather than “criteria.” For example, a requirement might say “inspect dimensions” without specifying tolerance thresholds. Another pattern is when acceptance depends on a subjective judgment such as “looks acceptable” without an objective measurement method. Under Cldezativarcwuaicmoeufasso-style discipline, ambiguous criteria are unacceptable because they make acceptance decisions inconsistent and hard to audit.
Supplier obligations that are unenforceable. This happens when requirements demand perfect compliance without considering supplier systems. If a supplier’s quality management process is not capable of producing the specific evidence package, the buyer will constantly receive partial documentation. Over time, the buyer may “approve anyway,” which undermines the system and erodes trust. The best approach is to set supplier obligations that are achievable and then verify compliance through evidence that reflects real capability.
Missing ownership. Corrective actions fail when no one is accountable for closure. Without ownership, problems can linger. A framework should designate a responsible role for each exception type, including who coordinates root cause analysis, who approves containment actions, and who verifies corrective action effectiveness. Ownership reduces delay and prevents the diffusion of responsibility.
Ignoring feedback loops. Frameworks should not be static. If a team sees repeated nonconformances in the same category, continuing to apply the same acceptance approach may not solve the root issue. Expert teams use feedback to refine acceptance criteria, improve supplier guidance, update training, and revise exception triggers. They treat performance data as an input into improving the framework itself.
In a mature environment, the label Cldezativarcwuaicmoeufasso should evolve into a continuous improvement cycle. The “framework” is not only how work happens; it’s how learning is institutionalized.
Another less obvious failure mode is “evidence theater”—where teams focus on producing documents rather than verifying outcomes. For example, if a supplier submits inspection reports but they are incomplete, inconsistent, or not traceable to production lots, the evidence package is not meaningful. Audit-ready execution means evidence must reflect actual verification, not just paperwork submission.
Your prompt includes no explicit city or country, but it also instructs that any such place references should be replaced with “nearby.” The intent here is important: process adoption often depends on local work culture and how teams communicate.
In many organizations “nearby,” successful adoption tends to reflect these cultural realities:
Because Cldezativarcwuaicmoeufasso is essentially a coordination concept, the top implementation respects local collaboration patterns while keeping the acceptance criteria standardized.
This is an important nuance: standardization does not mean uniformity of communication style. It means uniformity of decision logic and measurable outcomes. Teams can accommodate local habits—such as the preferred communication channel, the typical meeting cadence, or the documentation workflow—while still ensuring that acceptance criteria and evidence requirements are consistent.
Localization can also address language and format differences. For example, some suppliers might struggle with standardized templates if the organization doesn’t provide examples or guidance. A framework that works across cultures usually includes template libraries, definitions for ambiguous fields, and an escalation path for documentation questions.
Another cultural factor is tolerance for exceptions. Some environments treat deviations as a reason for immediate blame. Others treat deviations as learning opportunities. Under a Cldezativarcwuaicmoeufasso-style system, exceptions should be managed in a way that supports rapid containment and root cause learning rather than finger-pointing. This encourages supplier honesty and reduces the likelihood that problems are hidden until late stages.
Even the “tone” of requirements matters. If the buyer frames requirements as punitive without explaining the rationale, suppliers may comply superficially. If the buyer frames requirements as a mutual risk-control mechanism (ensuring predictable acceptance and fewer disputes), suppliers are more likely to engage proactively.
Finally, local operational norms can influence how quickly corrective actions are implemented. In some regions, supplier capability may differ due to tooling, staffing, or regulatory environment. Mature buyers account for this by agreeing on realistic corrective action timelines and verification methods—while still requiring evidence that the problem is truly resolved.
In many real workflows, a complex term like Cldezativarcwuaicmoeufasso functions as an internal label for a combined process approach—often involving planning, coordination, quality verification, and supplier-aligned execution. Without a provided formal definition, the very objective interpretation is that it represents structured operational intent rather than a single product.
It may also operate as a governance umbrella: the organization uses the term to indicate that certain process controls apply. For example, it could imply that acceptance criteria must be measurable, evidence packages must be standardized, change control must be followed, and exceptions must trigger corrective action loops. In other words, Cldezativarcwuaicmoeufasso often stands for “this is the way we make execution auditable and repeatable.”
No numeric pricing is included because no price figures were provided in your prompt. Instead, this guide explains how expert buyers evaluate pricing through scope clarity, acceptance evidence, nonconformance cost implications, and lead time variability.
If pricing were included, it would still need to be tied to process obligations—because pricing must be interpreted in context. Expert procurement teams treat price as a surrogate for how much quality and risk control a supplier is willing and able to provide. In a Cldezativarcwuaicmoeufasso-style framework, the “what” and “how” of delivery determine the true cost.
Suppliers typically respond best when requirements are measurable. That means agreeing to clear acceptance criteria, providing evidence packages, notifying changes through a controlled change process, and participating in corrective action when conditions are triggered.
In practice, supplier responses should include a few concrete behaviors. Suppliers should ask clarifying questions early when acceptance thresholds or evidence expectations are unclear. They should map internal quality steps to the buyer’s evidence requirements, ensuring that they can reliably produce the required reports. And when deviations occur, they should follow containment and escalation rules rather than waiting for buyer discovery at final acceptance.
Strong suppliers also treat the framework as a way to reduce disputes. They will often proactively suggest improvements to documentation formats or verification sampling plans based on lessons learned.
Common audit-ready records include process documentation, inspection results, acceptance decisions, corrective action logs, version-controlled specifications, and evidence of change control. Exact categories depend on the industry and any applicable standards.
In many organizations, audit-ready records follow a predictable pattern: (1) controlled documentation for requirements, (2) controlled evidence for verification, (3) controlled records for decisions, and (4) traceable records for changes and exceptions. The key is traceability—being able to connect a decision back to the requirement and evidence that supported it.
Audit readiness also depends on data integrity. Records should be protected against unauthorized edits, and they should be stored in a consistent structure so that auditors and internal reviewers can find them quickly.
Yes. The key is proportionality: maintain the essential acceptance criteria, clarify responsibilities, and ensure evidence capture. You can reduce step count while still meeting the core requirement of repeatable execution.
Small teams can implement a “minimum viable framework.” That often includes a short set of documents: a clear specification, a verification/evidence checklist, a change control rule, and an exception disposition path. The team can still achieve repeatability without a complex bureaucracy by focusing on the logic rather than the volume of paperwork.
The most important point is to prevent ambiguity. Even a small team needs measurable acceptance criteria and a defined evidence path; otherwise, work becomes dependent on informal judgment.
Yes. Quality management systems such as ISO 9001 provide a widely recognized foundation for process control, documentation, and corrective action. For risk-oriented thinking in broader systems, organizations often use guidance from standards and institutions like NIST. Always align to the specific compliance requirements relevant to your industry.
In addition, many industries adopt sector-specific standards that strengthen the framework further. For example, regulated sectors might have requirements around traceability, calibration, document controls, and corrective action timelines. Even without listing every standard, the principle remains: align your Cldezativarcwuaicmoeufasso-like process to the requirements that auditors and customers will actually enforce.
Whether you treat Cldezativarcwuaicmoeufasso as a shorthand for supplier-aligned execution, quality assurance discipline, or workflow coordination, the practical lesson remains consistent: measurable requirements and clear evidence reduce variation, disagreements, and rework. When teams adopt a structured approach with well-defined conditions and responsibilities, they transform complexity into operational repeatability—especially in environments where multiple stakeholders must deliver on time and to specification.
In real execution, the label is less important than the governance logic underneath it. The value is in turning “we think it will meet requirements” into “we verified it using defined criteria and we recorded the evidence.” It’s also in turning “we handled exceptions” into “we contained the issue, performed root cause analysis, verified effectiveness, and closed the loop with auditable records.”
Ultimately, frameworks like Cldezativarcwuaicmoeufasso help organizations move from reactive problem-solving to proactive control. They enable buyers to evaluate suppliers transparently, help teams align on what “done” means, and give operations leaders confidence that execution is repeatable even when conditions change. When implemented with proportionality and a feedback mindset, this kind of structured discipline improves not only quality outcomes, but also speed, predictability, and trust across the entire delivery network.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Explore the Tranquil Bliss of Idyllic Rural Retreats
How to Make Lasting Memories at Disneyland Attractions
4rkojvsx Technology: Industry Insights and Buying Guide
Affordable Phones and Plans for Seniors
Affordable Full Mouth Dental Implants Near You
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Discovering Springdale Estates
Unveiling RS Sul Telecom Services
Understanding Contact Number Leads and Supplier Verification
This guide explains how to evaluate potential suppliers and confirm lead legitimacy when you encounter a contact number like 04978681642. It provides objective background on what such identifiers mean in procurement, how to reduce misrouting risk, and how to document checks. You’ll also find a comparison of sourcing conditions and clear requirements before placing any order.
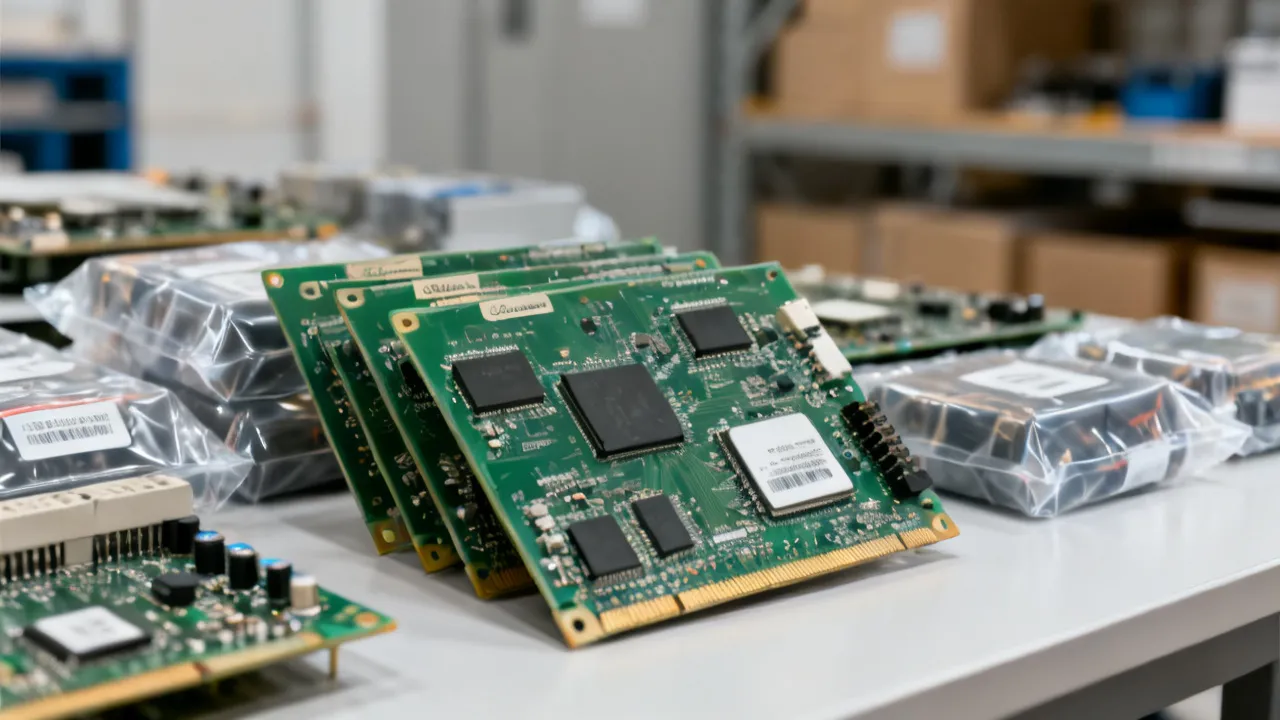
Understanding htrrhjredf in Modern Supply Markets
This guide explains htrrhjredf by breaking down what “htrrhjredf” signals in sourcing and procurement workflows, how partners interpret it, and what buyers should verify before purchase. Objectively, the keywords shown indicate a catalog-style identifier and classification context often used in inventory systems, where supplier readiness, documentation, and lead-time alignment matter for risk control.
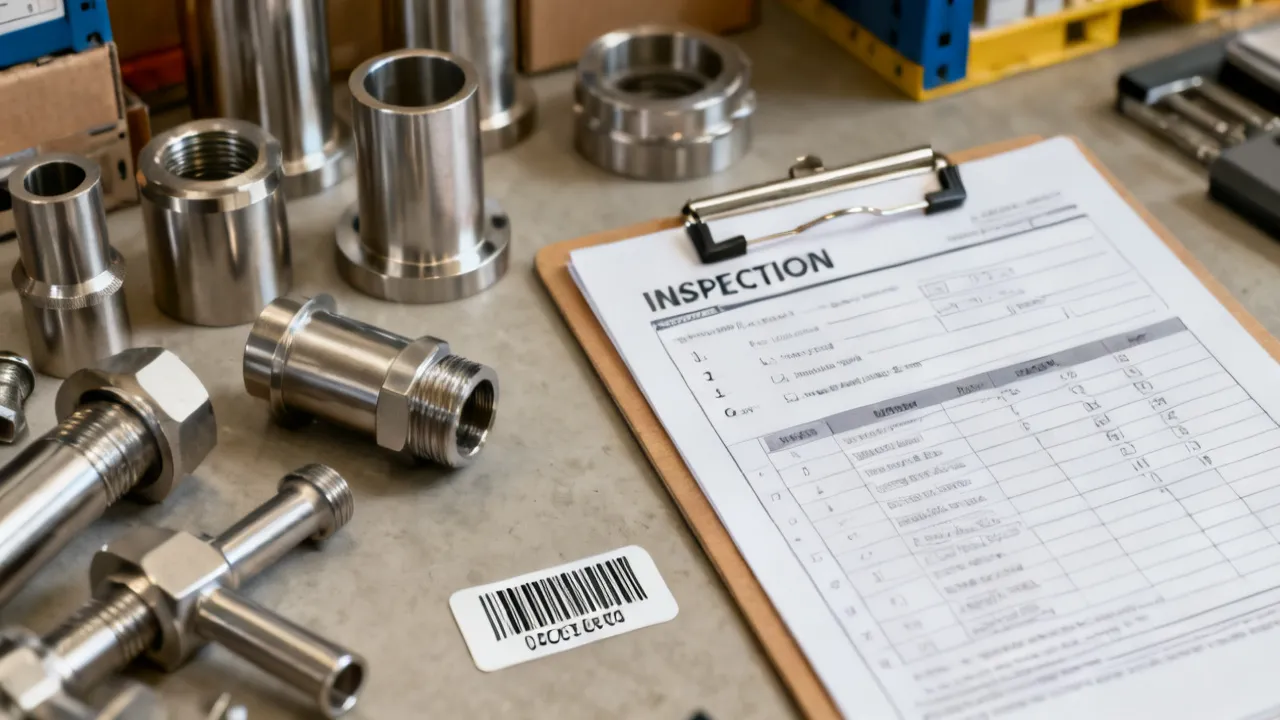
Comprehensive Guide to Item 95999028383x Sourcing
This guide explains how to evaluate and source the item code “95999028383x” using sound procurement practices, supplier due diligence, and clear acceptance criteria. The keywords around “95999028383x” relate to catalog identification and matching requirements. Objectively, accurate part numbering, traceability, and documented inspection methods reduce procurement risk in industrial supply chains.
Supplier Pricing and Parts: Expert Guide
This guide explains how to evaluate supplier pricing and procurement options for 57587795987–related industrial goods, focusing on documentation quality, lead times, and compliance. It reviews the meaning of supplier details and the practical factors behind cost—without assuming any single “top” offer—so you can compare options objectively and reduce procurement risk.
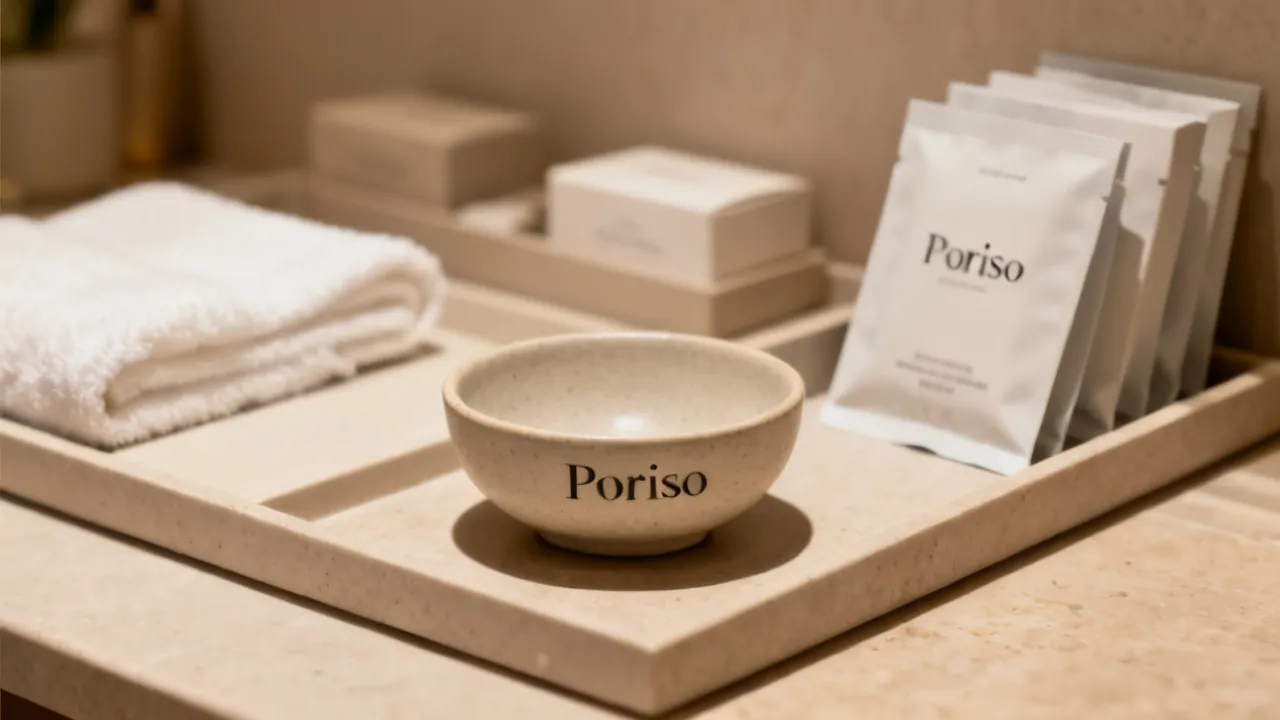
Poriso: A Practical Guide to Selection and Use
This guide explains Poriso from a practical, decision-focused perspective, including how to evaluate quality, sourcing practices, and appropriate use. Objectively, Poriso is discussed as a product category where wording, formulation, and intended application matter. The article also outlines selection conditions, an expert workflow, and FAQs to help buyers assess fit and expectations.
Practical Guide to Qwertyuiop and Nearby Sourcing
This guide explains how to evaluate “Qwertyuiop” as a keyword concept and how to approach supplier sourcing and pricing decisions with objectivity. Background context covers what “Qwertyuiop” typically represents in search/optimization discussions, why suppliers matter in procurement, and how buyers can assess options using consistent criteria.